📊 Full opportunity report: Cybersecurity operations signal monitor: A backdoor in a LinkedIn job offer on IdeaNavigator AI — validation score, market gap, and execution plan.

Get the latest gadgets delivered free — and shop member deals
- Fast, free delivery on millions of items
- Access to Prime Big Deal Days deals on October 6–7
- Prime Video, Amazon Music and more included
TL;DR
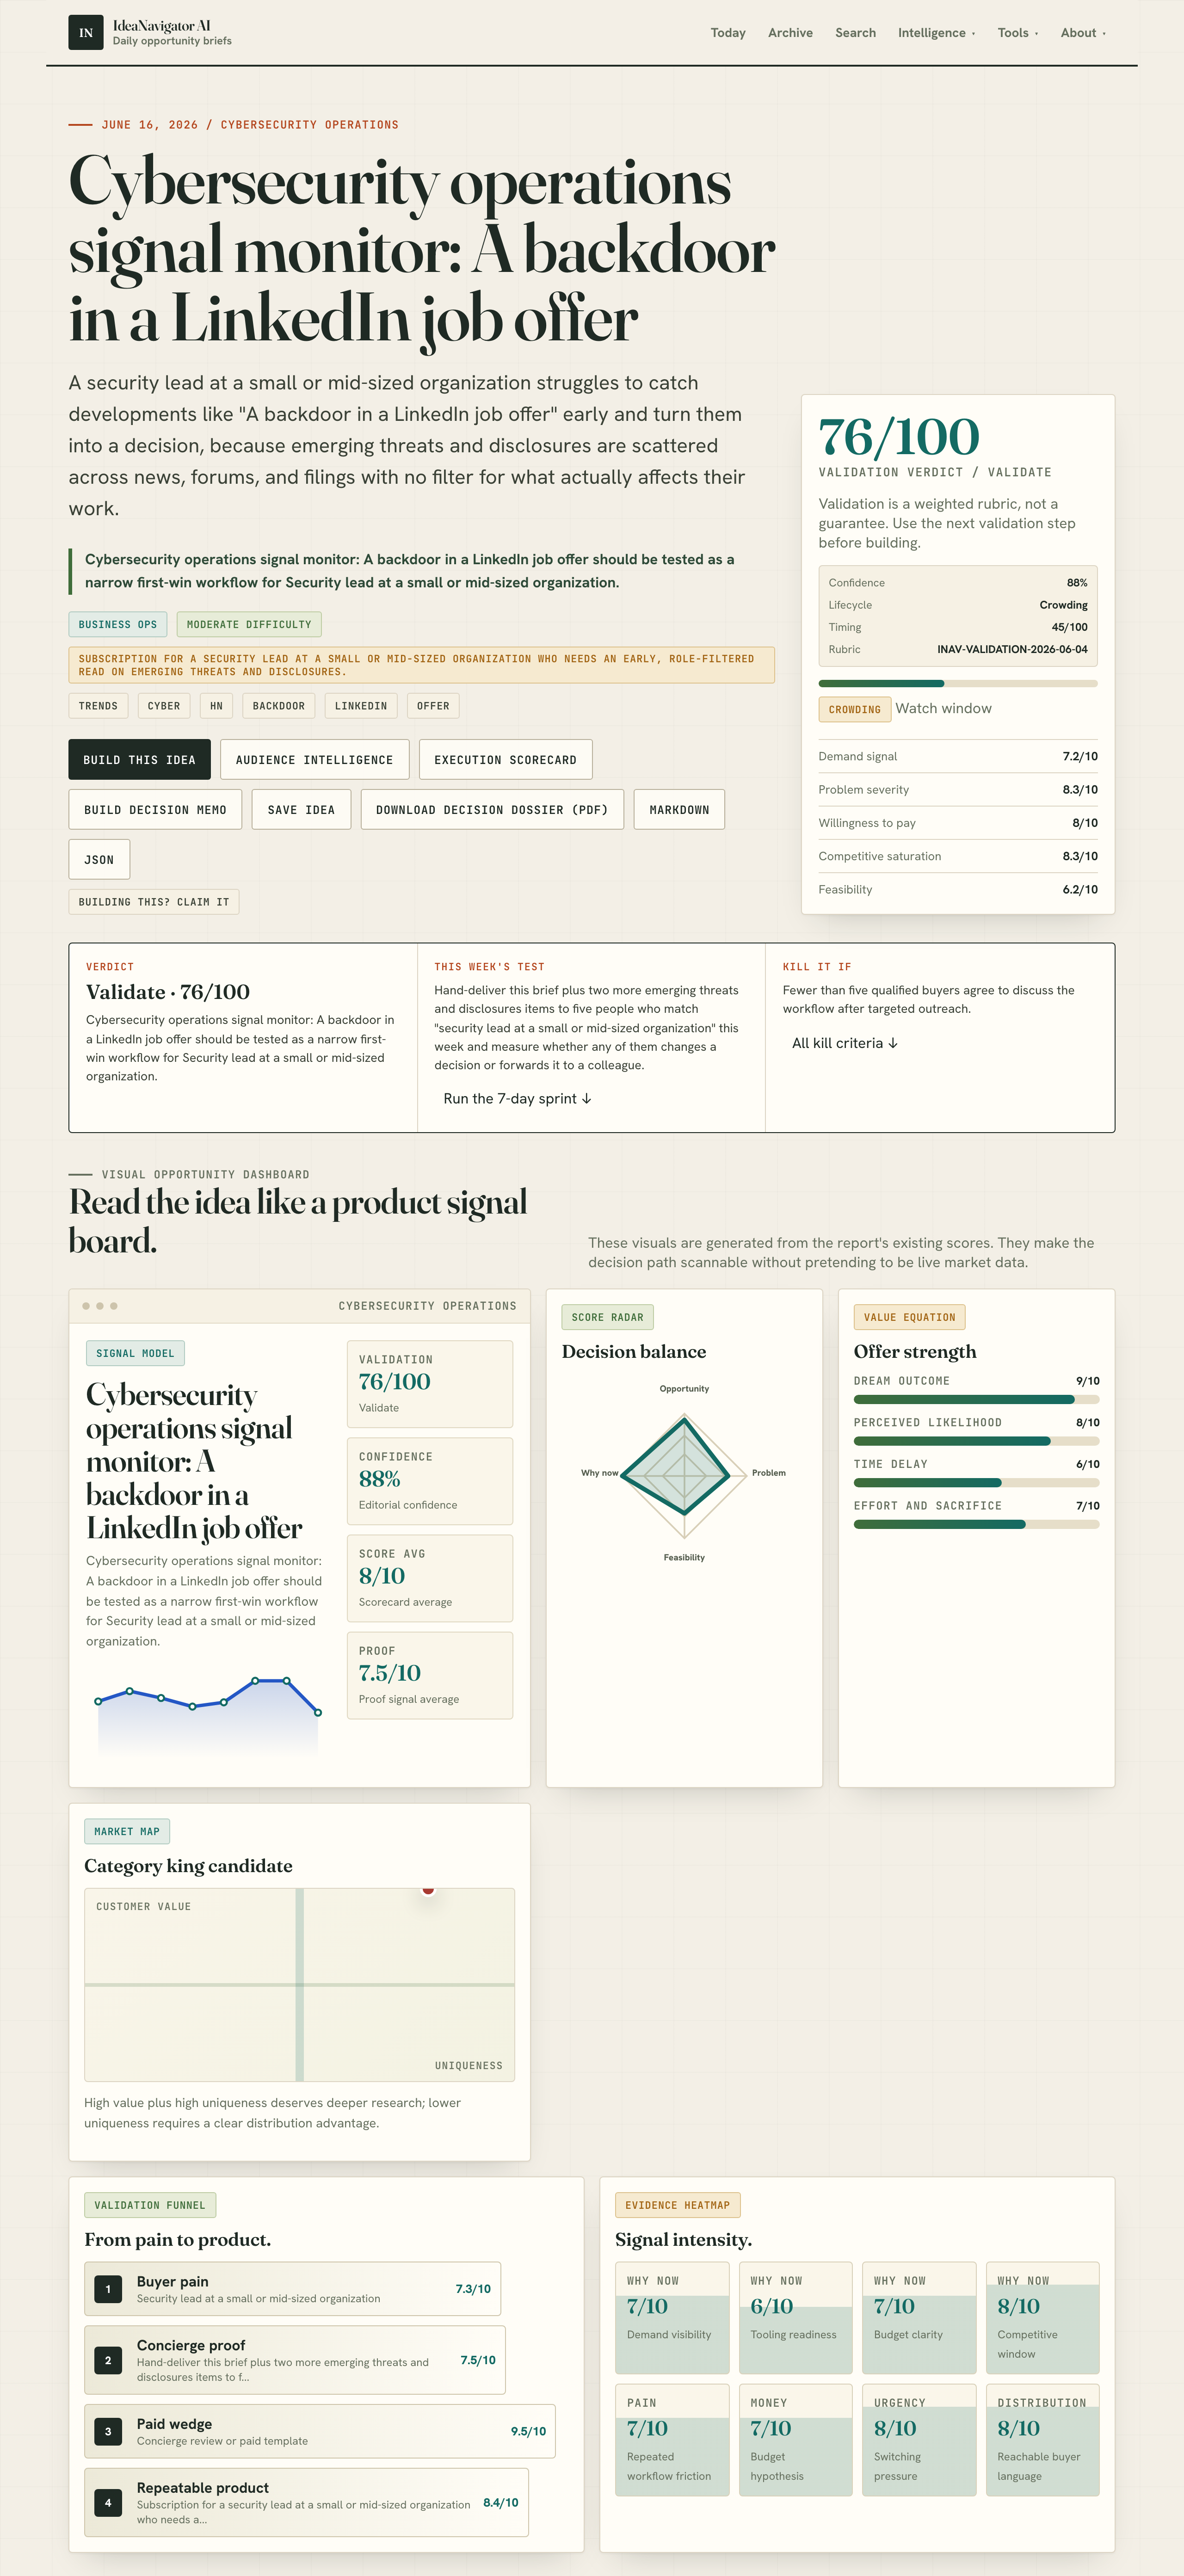
Cybersecurity analysts have confirmed the detection of a backdoor in a LinkedIn job offer. This development signals potential targeted attacks and highlights the need for vigilance in hiring processes.
Cybersecurity researchers have confirmed the discovery of a backdoor embedded in a LinkedIn job offer, signaling a potential targeted threat to organizations and individuals. The finding underscores the importance of scrutinizing online job postings for malicious code, especially as threat actors increasingly use social platforms for infiltration.
The backdoor was identified by cybersecurity analysts monitoring emerging threats on platforms like Hacker News. It was embedded within a job offer posted on LinkedIn, designed to exploit unsuspecting applicants or recruiters. The threat was detected through specialized analysis of the posting’s code and metadata, which revealed malicious scripts capable of establishing unauthorized access to targeted systems.
According to cybersecurity experts involved in the investigation, the backdoor appears to be part of a broader campaign aimed at small and mid-sized organizations, which often lack extensive security measures. The specific malware payload has not yet been fully analyzed, but initial reports suggest it could enable remote access, data exfiltration, or further exploitation.
Implications for Organizational Security and Hiring Practices
This discovery highlights a new vector for cyberattacks leveraging social media platforms, particularly LinkedIn, which is widely used for recruiting. Organizations need to be aware that malicious actors are embedding backdoors in seemingly legitimate job postings, potentially leading to targeted compromises. For security leads at small and mid-sized firms, this underscores the importance of vetting online job offers and implementing monitoring for suspicious activity related to recruitment channels.
cybersecurity threat detection software
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Over recent years, cybercriminals have increasingly used social engineering tactics to infiltrate organizations, often exploiting the trust placed in online job postings. Previous incidents have involved malicious attachments, phishing links, and compromised profiles. The current finding of a backdoor in a LinkedIn job offer indicates that threat actors are refining their methods, embedding malicious code directly into recruitment advertisements to target specific organizations or individuals.
network monitoring tools for small business
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Extent and Impact of the Backdoor Threat Unclear
It is not yet confirmed how widespread this type of backdoor is or whether it has been actively exploited in targeted attacks. The full technical details of the malicious code are still under analysis, and it remains unclear which organizations or individuals may have been affected so far. Further investigation is needed to assess the scope and potential damage.
As an affiliate, we earn on qualifying purchases.
Monitoring and Mitigation Strategies Underway
Cybersecurity teams are working to analyze the malicious payload and develop detection signatures. Organizations are advised to review their recruitment-related communications and employ monitoring tools to flag suspicious activity linked to LinkedIn job postings. Future updates will clarify the extent of the threat and recommended mitigation steps.
As an affiliate, we earn on qualifying purchases.
Key Questions
How can I identify if a LinkedIn job offer contains a backdoor?
Look for unusual scripts or code embedded in the job posting, and verify the authenticity of the posting through official channels. Employ security tools that scan links and attachments for malicious content.
What should organizations do if they suspect a backdoor in a job posting?
Immediately isolate affected systems, notify cybersecurity teams, and conduct a thorough investigation. Report the suspicious posting to LinkedIn and relevant authorities.
While this incident involves LinkedIn, similar tactics could be used on other social media and recruitment platforms. Vigilance across all channels is recommended.
Are there known cases of organizations being compromised through such backdoors?
Specific cases are still under investigation, but threat actors have previously exploited social media posts to gain initial access in targeted attacks.
Source: IdeaNavigator AI
Fall Picks
fall essentials
As an affiliate, we earn on qualifying purchases.